Posts tonen met het label be warned. Alle posts tonen

20140103

World of Warcraft users warned of malware that steals account, authenticator data

[~Time Published January 03, 2014 at 04:30PM]

*/*/*/*/*/\*\*\*\*\*


World of Warcraft players are being advised to be vigilant of a "dangerous Trojan" that could potentially compromise their accounts, even if they are using a Battle.net authenticator to protect themselves.

According to a post on Blizzard's support forum, the reported malware acts in real time by "stealing both your account information and the authenticator password at the time you enter them." Both the mobile and physical Battle.net authenticator are identified as at-risk.

Blizzard support reps said the Trojan can be identified by creating an MSInfo file and then looking in the Startup Program section of that file for either "Disker" or "Disker64." The malware cannot be spotted until after it becomes active and no known security...

Continue reading…


*/*/*/*/*/View@Source\*\*\*\*\* (http://www.polygon.com/2014/1/2/5267872/world-of-warcraft-users-warned-of-malware-that-steals-account)


[IFTTTautoSHAREv1.015 | Shared with ifttt.com More shared news etc on: http://bit.ly/Schavuiten_blog | RSS source: http://theoldreader.com/profile/51411ac5bd9279fddb0009c6]

20140102

Not So Anonymous VPN Uses Edward Snowden For PR

[Time Published January 02, 2014 at 08:54PM]

*/*/*/*/*/\*\*\*\*\*

HMA-logo Over the past couple of months the revelations of Edward Snowden’s leaks have dominated the news.

As a result, interest in anonymity services such as Tor and VPNs has increased as even regular Internet users don’t like the idea of being monitored.

The increased demand for privacy has given an enormous boost to many VPN providers, many of which claim they can protect users from the prying eyes of “monitoring” outfits, to a certain degree.

One VPN service takes its response one step further, as it explicitly uses Snowden’s name for PR purposes. As can be seen below, the popular VPN HideMyAss lists a screenshot of an account with the username ESnowden in the App Store.

This ESnowden is apparently trying to connect to a United States IP-address from Russia, a reference to the current location of the NSA leaker.


ESnowden using HideMyAss

HMA-screenshot

While this type of PR isn’t particularly tasteful, it’s also rather ironic since HideMyAss’ service does very little to keep users anonymous.

Two years ago HideMyAss made headlines all over the Internet when it became known that they were ordered to share the personal details of one of its users with the authorities. The user in question, the now-jailed LulzSec hacker Cody Kretsinger, was exposed by the VPN which he assumed would keep him safe.

This revelation got a discussion going about the logging policies of various providers, and it was the reason for us to provide an overview of VPN services that store no, or minimal logs.

HideMyAss certainly didn’t make it into this list. The company records the following identifiable information of its users according to its logging policy, which is then stored for a period of two to three months:

· a time stamp when you connect and disconnect to our VPN service;

· the amount data transmitted (upload and download) during your session;

· the IP address used by you to connect to our VPN; and

· the IP address of the individual VPN server used by you.


In other words, in terms of IP-logging HideMyAss doesn’t really offer more privacy than the average Internet provider.

While this is totally fine, since the company is transparent about its policies, using Edward Snowden’s name for their PR is a bit ironic. After all, if the authorities wanted to they could easily obtain Snowden’s IP-address from HideMyAss.

Perhaps this type of PR should serve as a reminder that not all VPNs are as anonymous as they appear to be.

Source: TorrentFreak, for the latest info on copyright, file-sharing and VPN services.


*/*/*/*/*/\*\*\*\*\*


[ Author: | Source: http://feed.torrentfreak.com/~r/Torrentfreak/~3/ULCAAf6SpMI/] | Image URL: http://torrentfreak.com/images/HMA-logo.jpg] [IFTTTautoSHAREv1.002 | Shared with ifttt.com More shared news etc on: http://bit.ly/Schavuiten_blog ]

20131102

Western Digital raadt klanten af te updaten naar OS X Mavericks

[Author: ]

[Time Published November 02, 2013 at 12:56PM]

[ < - - Content ] Western Digital raadt klanten met Apple-computers af te updaten naar OS X Mavericks. De fabrikant van onder meer externe harde schijven heeft klachten in onderzoek dat de update problemen veroorzaakt in combinatie met software van de fabrikant. [ - - > ]


[Source: http://tweakers.net/nieuws/92351/western-digital-raadt-klanten-af-te-updaten-naar-os-x-mavericks.html] | Image URL: http://ifttt.com/images/no_image_card.png]

20131023

Driver-bug uit juni BSOD't Windows 8.1-upgrades

[Author: ]

[Time Published October 23, 2013 at 02:34AM]

[ < - - Content ] Niet alleen Windows RT struikelt over upgraden naar 8.1. Ook x86-pc's gaan niet allemaal vlekkeloos over. Drivers lijken de oorzaak. [ - - > ]


[Source: http://webwereld.nl/it-beheer/79745-driver-bug-uit-juni-bsod-t-windows-8-1-upgrades] | Image URL: http://ifttt.com/images/no_image_card.png]

20131014

Google-Backed File-Sharing Service Spreads Malware

[Author: ]

[Time Published October 14, 2013 at 06:55PM]

[ < - - Content ]
xunlei To the Western public the name Xunlei might not ring any immediate bells, but in China its software is used by hundreds of millions of people every month.

Previously the company’s BitTorrent client was crowned the most used BitTorrent software in the world, beating uTorrent and several other popular clients.

Xunlei’s website offers a searchable index of billions of media files which users can download with the proprietary Xunlei software. The company is partly owned by Google and in recent years has evolved into the leading player in the online file-sharing space.

Recently, however, the company ran into trouble when people spotted suspicious software on their systems signed with a Xunlei security certificate. A thorough investigation from ESET now reveals that Xunlei the company has been spreading malware to Windows and Android users.

While it’s unclear how the application is distributed, the windows installer “INPEnhSetup.exe” that spreads the suspicious files is directly connected to the Chinese file-sharing giant. Besides the security certificate, the application also calls home to the Xunlei-owned domain kankan.com

Once the “dropper” is installed it loads an Office plugin which among other things downloads an Android application. This application is then installed on all Android devices that are connected to the computer, which subsequently installs several other seemingly harmless applications.

ESET looked at all the technical details of the software distributed by Xunlei and has categorized the application as a malicious program under the name Win32/Kankan.

“The use of a fake Office plugin to gain persistence, the ability to silently install Android applications, and the backdoor functionalities, confirm the validity of the concerns of Chinese users and explains why ESET detects this program as malicious, under the name Win32/Kankan,” ESET’s Joan Calvet writes.

“There are still some open questions, like the original infection vector and the exact reason the Android applications were installed,” he adds.

While it remains unclear whether Xunlei’s popular BitTorrent client was used to spread the malware, the company has admitted that its employees were responsible for the development and distribution of the suspicious software.

During a press conference Xunlei apologized for their mistakes. The company said that the personnel responsible were acting without permission and have since been fired.

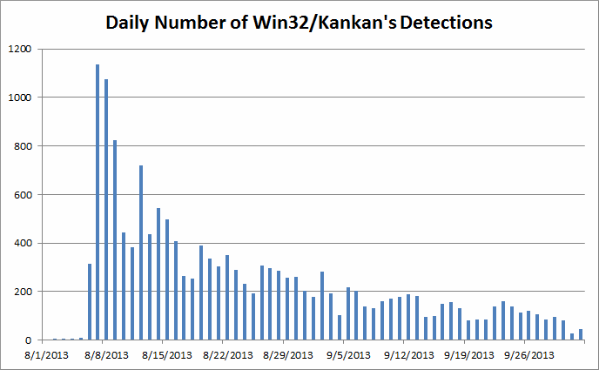
For affected users Xunlei has released an uninstaller and according to ESET the number of infections has dropped significantly since its release, as can be seen in the graph below.

detections
Source: Google-Backed File-Sharing Service Spreads Malware


[ - - > ]


[Source: http://torrentfreak.com/google-backed-file-sharing-spreads-malware-131014/] | Image URL: http://torrentfreak.com/images/xunlei1.jpg]

20131013

Hacker ontdekt backdoor in D-Link-routers

[Author: ]

[Time Published October 13, 2013 at 04:33PM]

[ < - - Content ] Een hacker heeft in de firmware van een aantal D-Link-routers een backdoor gevonden. Hierdoor is het mogelijk om zonder wachtwoord de admin-interface te benaderen en routerinstellingen te wijzigen. [ - - > ]


[Source: http://tweakers.net/nieuws/91902/hacker-ontdekt-backdoor-in-d-link-routers.html] | Image URL: http://ifttt.com/images/no_image_card.png]

20130925

‘Get rich quick’ scams hit Bitcoin

[Author: ]

[Time Published September 25, 2013 at 04:42PM]

[ < - - Content ]
Back in August, weird ads began appearing for something called the Bitcoin Robot that purported to earn massive profits by making hundreds of small transactions a day in the virtual currency, a version of the lucrative high-frequency trading done on Wall Street. The Bitcoin Robot claimed to have a waiting list of 20,000, even though the promo video through which it debuted has fewer than 500 views. Four days after launch, the Bitcoin Robot advertised that "EVERY Bitcoin Robot User Is In Profit (100% Success Quote) I-N-S-A-N-E!"

The Bitcoin Robot bears all the marks of a scam, down to the obviously fake affiliate reviews posted around the web and the illustrated 1-2-3 steps of "download, install, profit." The original ad even seemed to...

Continue reading…

[ - - > ]


[Source: http://www.theverge.com/2013/9/25/4767768/get-rich-quick-bitcoin-scams-bitcoin-robot] | Image URL: http://cdn2.sbnation.com/entry_photo_images/9022093/btc_robot_screen_shot_large.png]