[~Time Published January 12, 2014 at 07:37PM]
*/*/*/*/*/\*\*\*\*\*
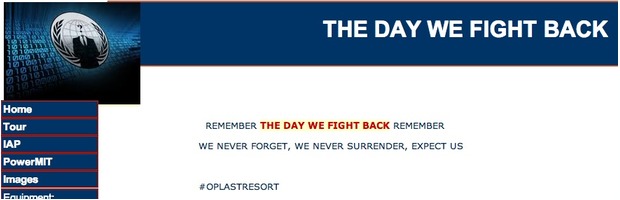
Anonymous defaced MIT's SSL-enabled Cogeneration Project page on Friday night, displaying a page that called viewers to “Remember the day we fight back.” “The day we fight back” references a protest planned for February 11 in opposition to surveillance and remembering Internet activist Aaron Swartz. The protest is backed by the EFF, Demand Progress, reddit, and Mozilla, among other big players in Internet culture.The defacement no longer appears on the site, but cogen.mit.edu was down as of Saturday morning.
One year ago on Friday, Aaron Swartz killed himself in what his parents and peers consider to be the act of a person bullied by federal prosecutors, who were suing Swartz for logging into MIT's network to gain access to the JSTOR database. Swartz downloaded millions of academic journal articles, and when he was caught, the federal government charged him with wire fraud, computer fraud, unlawfully obtaining information from a protected computer, and recklessly damaging a protected computer. Prosecutors told Swartz that he could face “up to 35 years in prison.”
Bob Swartz, Aaron's father, has been very vocal about implicating MIT in the suicide of his son, as well. In an interview published this month, Bob Swartz spoke with Boston Magazine about MIT's complicity in Aaron's harsh prosecution, from aiding Secret Service in cracking Aaron's computer to refusing to publicly state that it didn't want jail time for Aaron. “I always felt that MIT would act in a reasonable and compassionate way and that MIT wasn’t the issue... I didn’t understand the depths of what MIT had done at that point,” Swartz told Boston Magazine.
Read 1 remaining paragraphs | Comments


*/*/*/*/*/View@Source\*\*\*\*\* (http://feeds.arstechnica.com/~r/arstechnica/index/~3/NdmkotUGyZc/)
[IFTTTautoSHAREv1.015 | Shared with ifttt.com More shared news etc on: http://bit.ly/Schavuiten_blog | RSS source: http://theoldreader.com/profile/51411ac5bd9279fddb0009c6]
*/*/*/*/*/\*\*\*\*\*
ZDNet
Anonymous defaced MIT's SSL-enabled Cogeneration Project page on Friday night, displaying a page that called viewers to “Remember the day we fight back.” “The day we fight back” references a protest planned for February 11 in opposition to surveillance and remembering Internet activist Aaron Swartz. The protest is backed by the EFF, Demand Progress, reddit, and Mozilla, among other big players in Internet culture.The defacement no longer appears on the site, but cogen.mit.edu was down as of Saturday morning.
One year ago on Friday, Aaron Swartz killed himself in what his parents and peers consider to be the act of a person bullied by federal prosecutors, who were suing Swartz for logging into MIT's network to gain access to the JSTOR database. Swartz downloaded millions of academic journal articles, and when he was caught, the federal government charged him with wire fraud, computer fraud, unlawfully obtaining information from a protected computer, and recklessly damaging a protected computer. Prosecutors told Swartz that he could face “up to 35 years in prison.”
Bob Swartz, Aaron's father, has been very vocal about implicating MIT in the suicide of his son, as well. In an interview published this month, Bob Swartz spoke with Boston Magazine about MIT's complicity in Aaron's harsh prosecution, from aiding Secret Service in cracking Aaron's computer to refusing to publicly state that it didn't want jail time for Aaron. “I always felt that MIT would act in a reasonable and compassionate way and that MIT wasn’t the issue... I didn’t understand the depths of what MIT had done at that point,” Swartz told Boston Magazine.
Read 1 remaining paragraphs | Comments
*/*/*/*/*/View@Source\*\*\*\*\* (http://feeds.arstechnica.com/~r/arstechnica/index/~3/NdmkotUGyZc/)
[IFTTTautoSHAREv1.015 | Shared with ifttt.com More shared news etc on: http://bit.ly/Schavuiten_blog | RSS source: http://theoldreader.com/profile/51411ac5bd9279fddb0009c6]